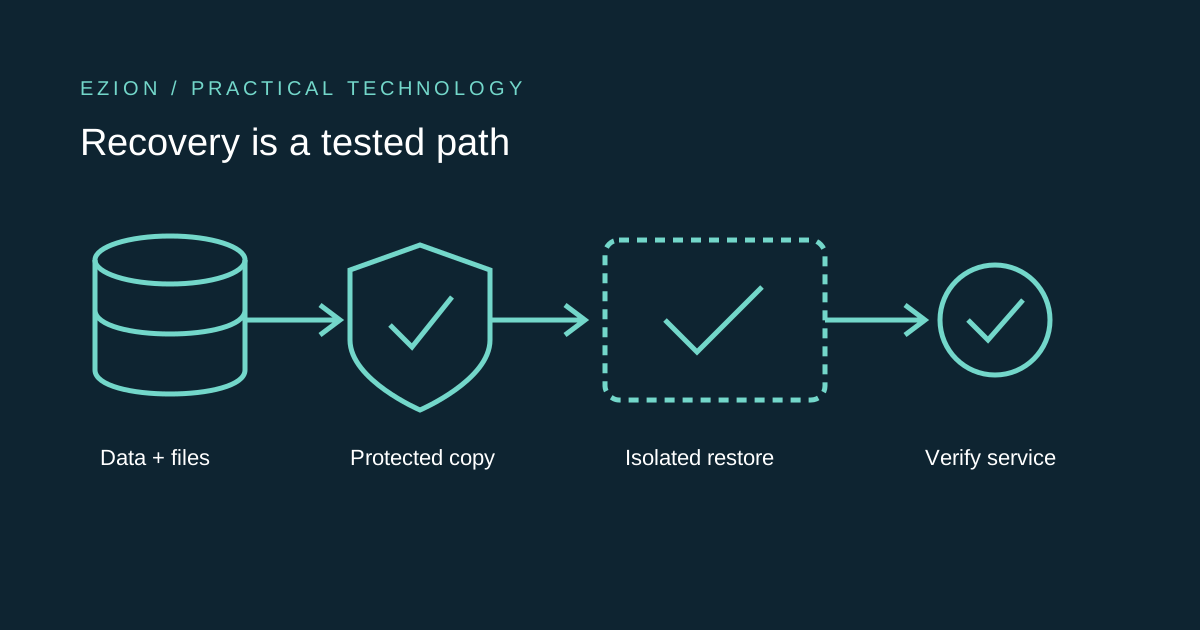
Backups That Survive a Restore Test: A Practical Recovery Plan
A green backup job is not proof of recovery. Define acceptable data loss, protect the backup boundary and rehearse a complete application restore.
Read article
Ezion / Tech
Practical notes on how AI changes the way people work, choose tools and manage risk—plus occasional software, cloud, security and wider technology topics when they change the decision in front of us.
A green backup job is not proof of recovery. Define acceptable data loss, protect the backup boundary and rehearse a complete application restore.
Read article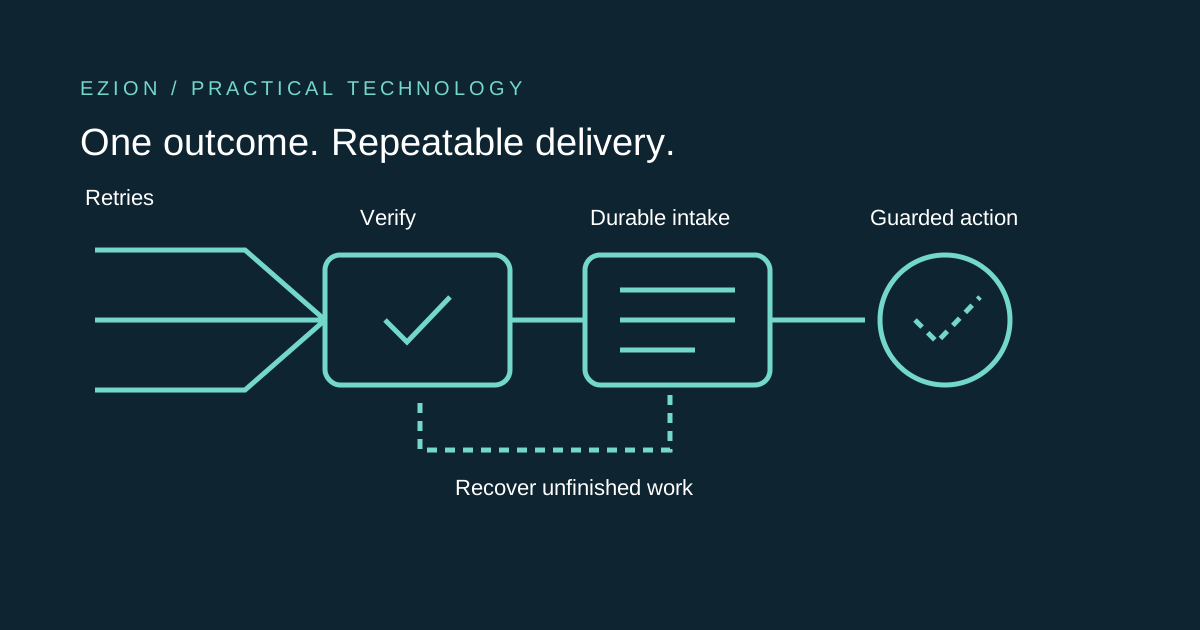
Use Stripe’s documented delivery behaviour to design verified intake, durable processing and replay-safe business actions without assuming event order.
Read article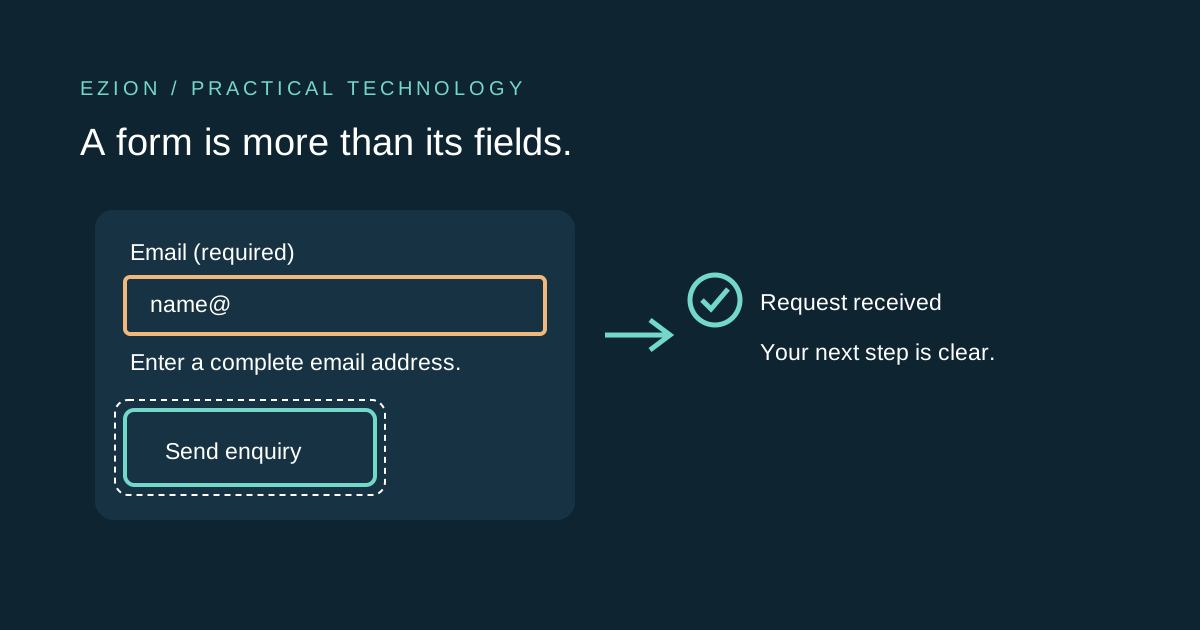
Build better enquiry and booking forms with native labels, useful instructions, recoverable validation and clear submission feedback—not a new component library.
Read article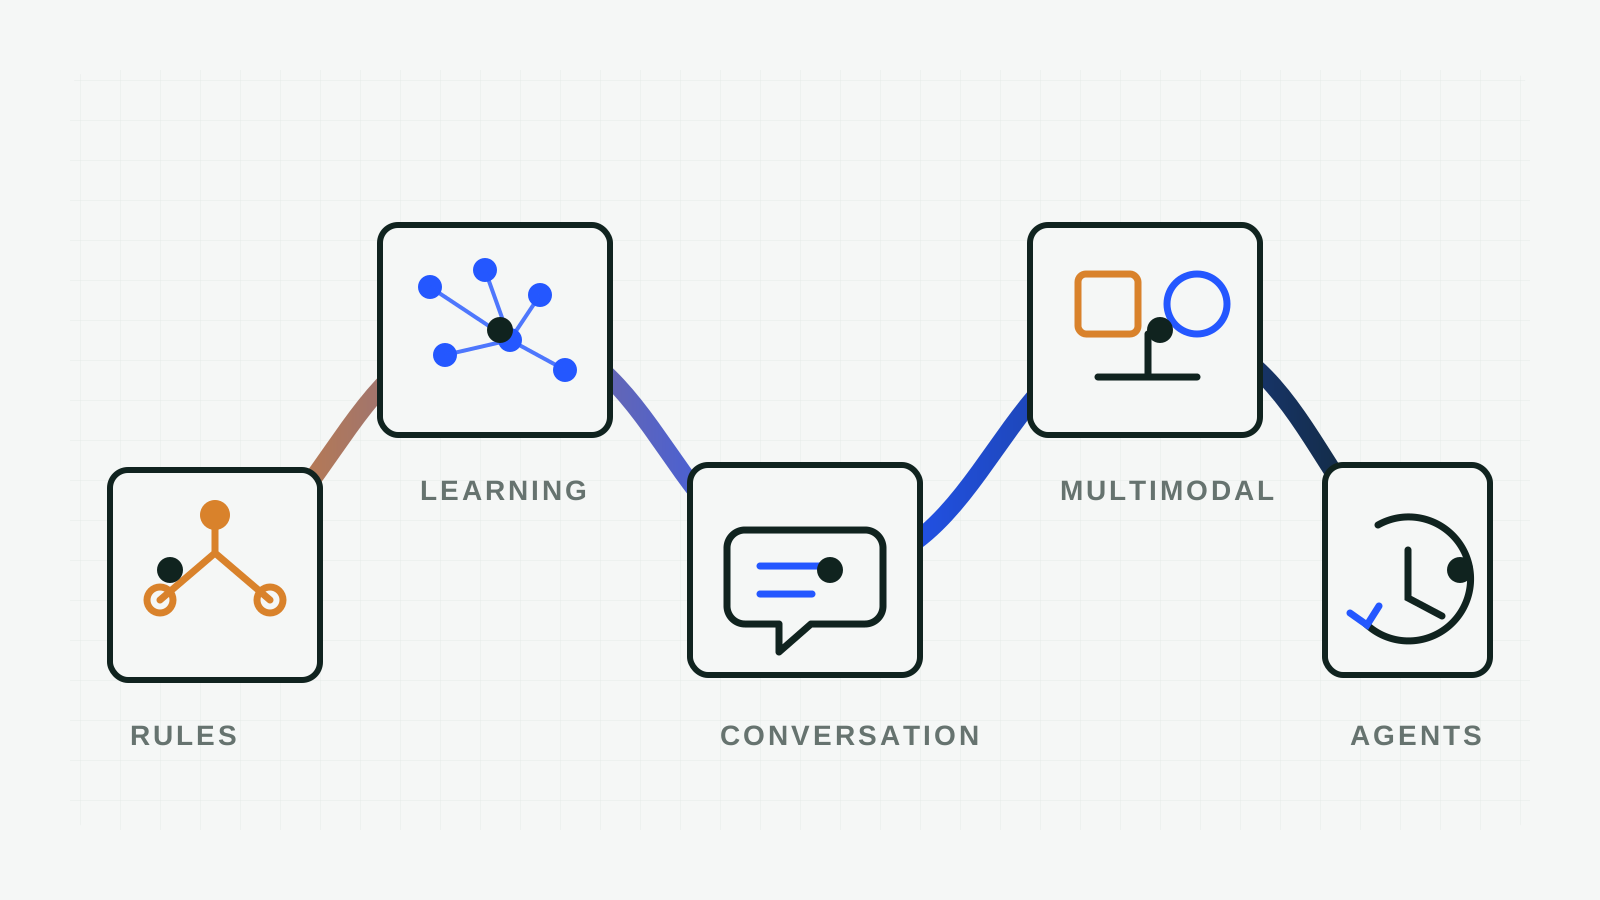
A practical history of AI interfaces—from specialist systems to chat, multimodal assistants and agents—and what each shift changed for the person using the tool.
Read article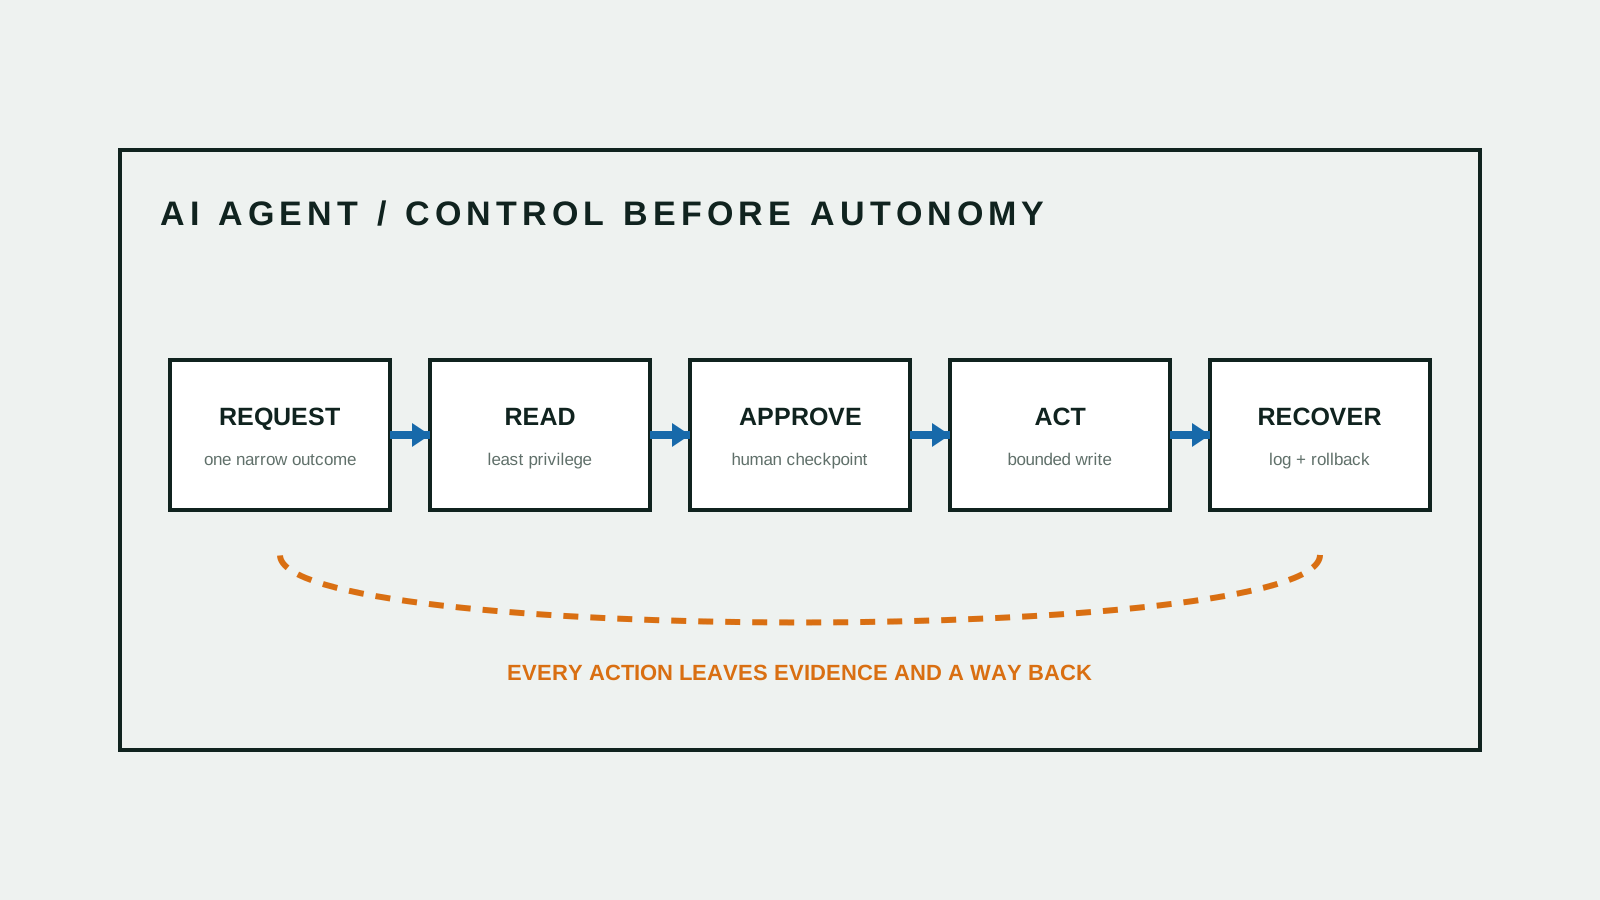
A practical control model for using AI agents without turning a helpful workflow into an unbounded Production operator.
Read article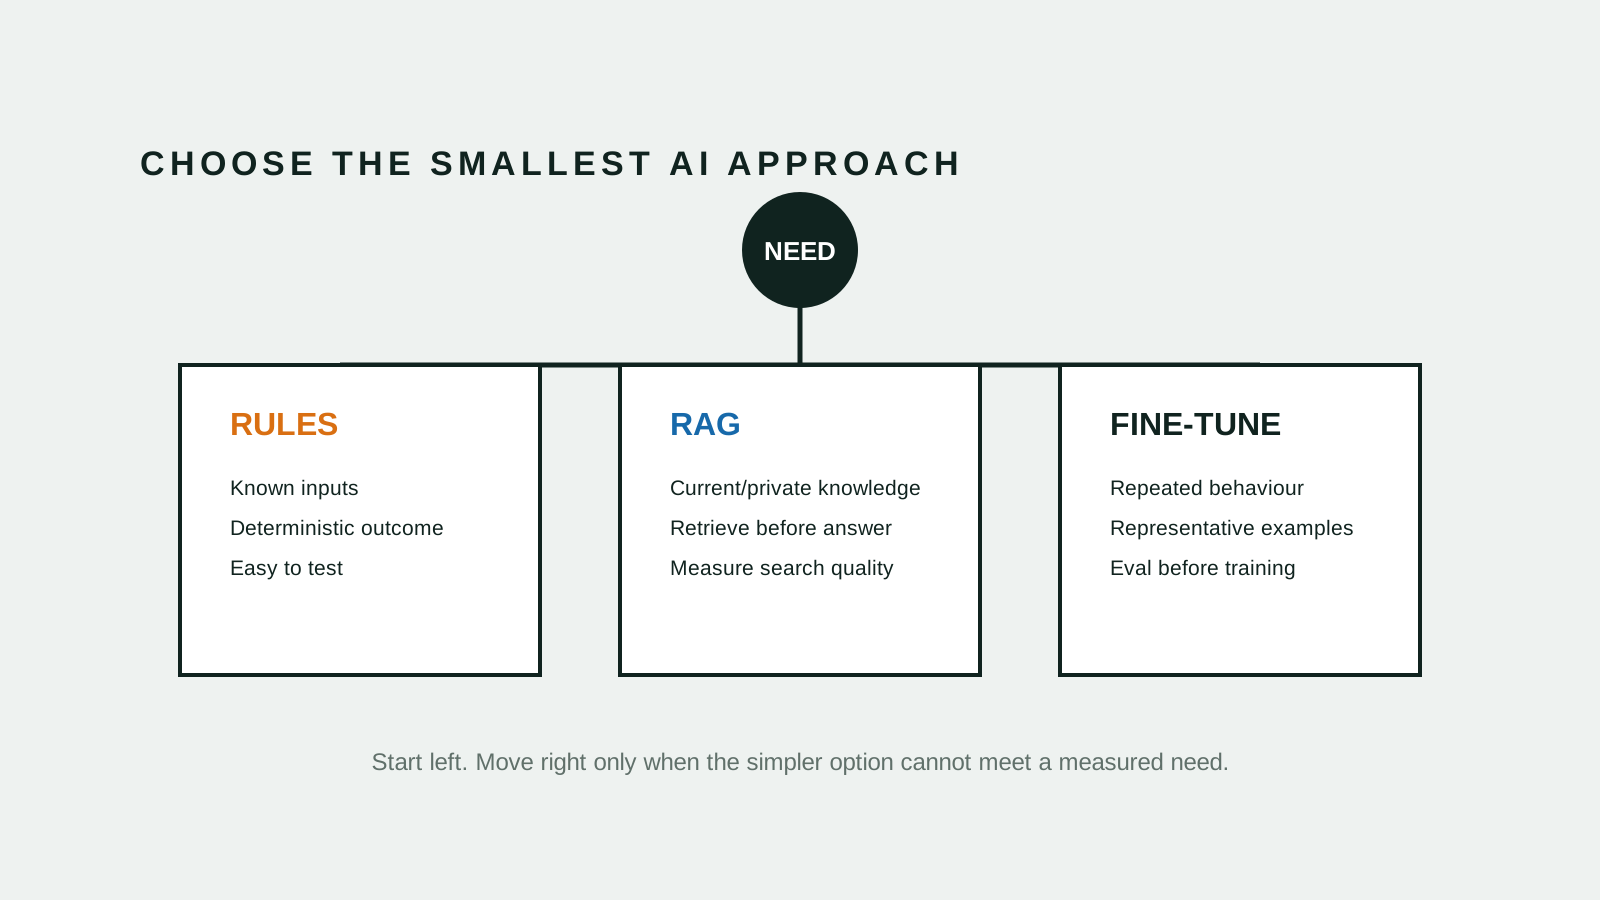
A decision guide for choosing deterministic workflow rules, retrieval-augmented generation or fine-tuning without making the solution larger than the problem.
Read article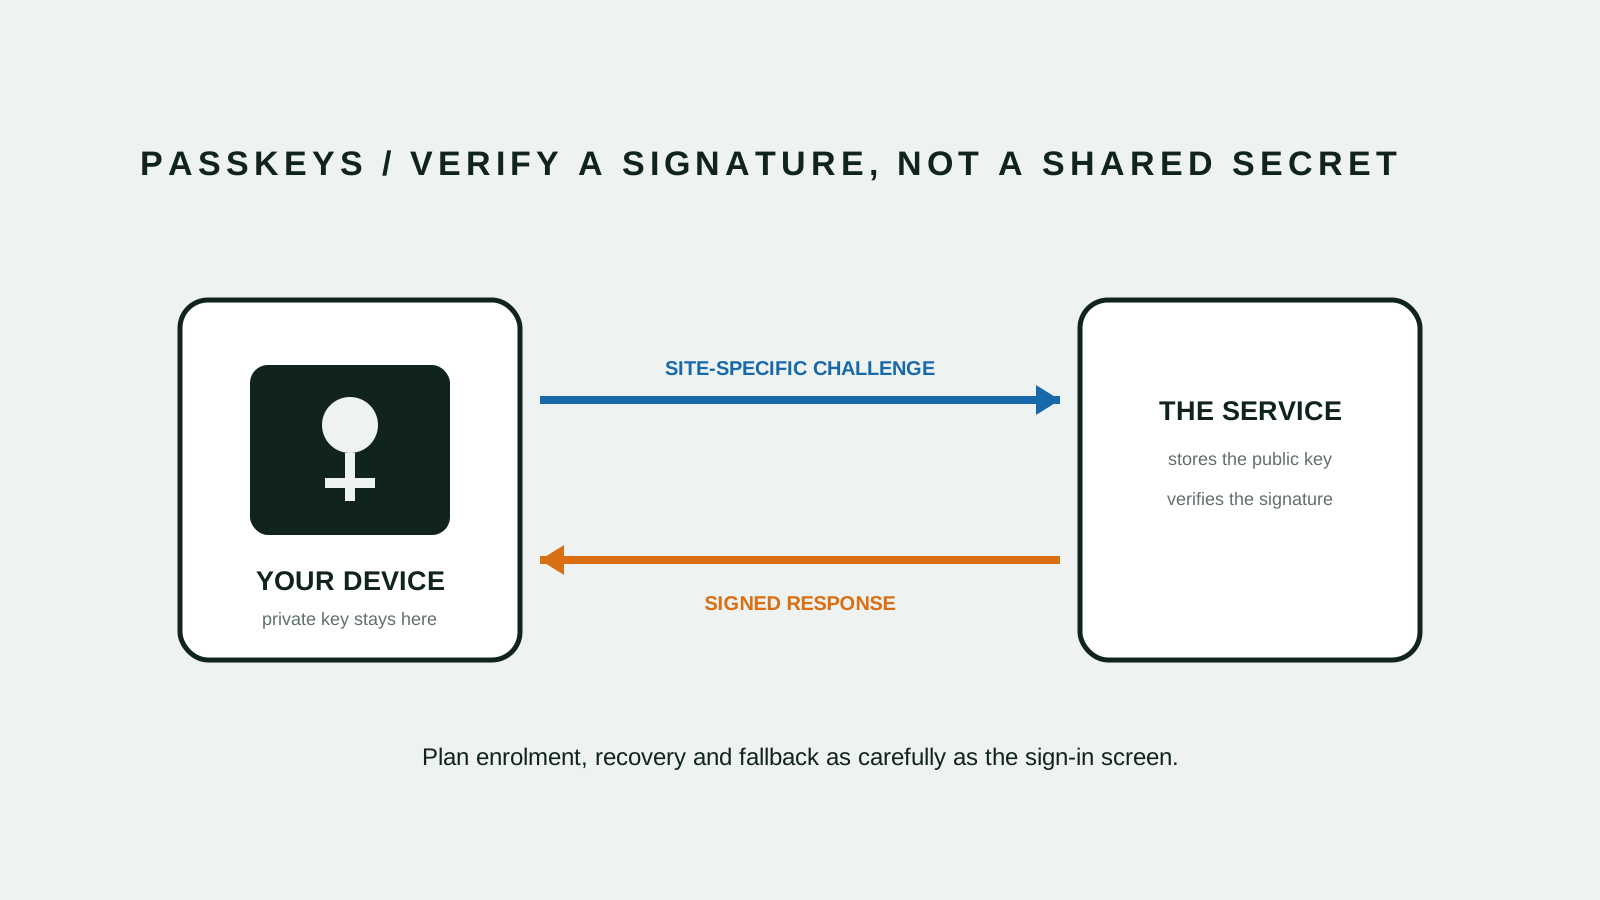
Passkeys replace a shared password with site-bound public-key credentials, but a safe rollout still depends on enrolment, recovery and fallback design.
Read article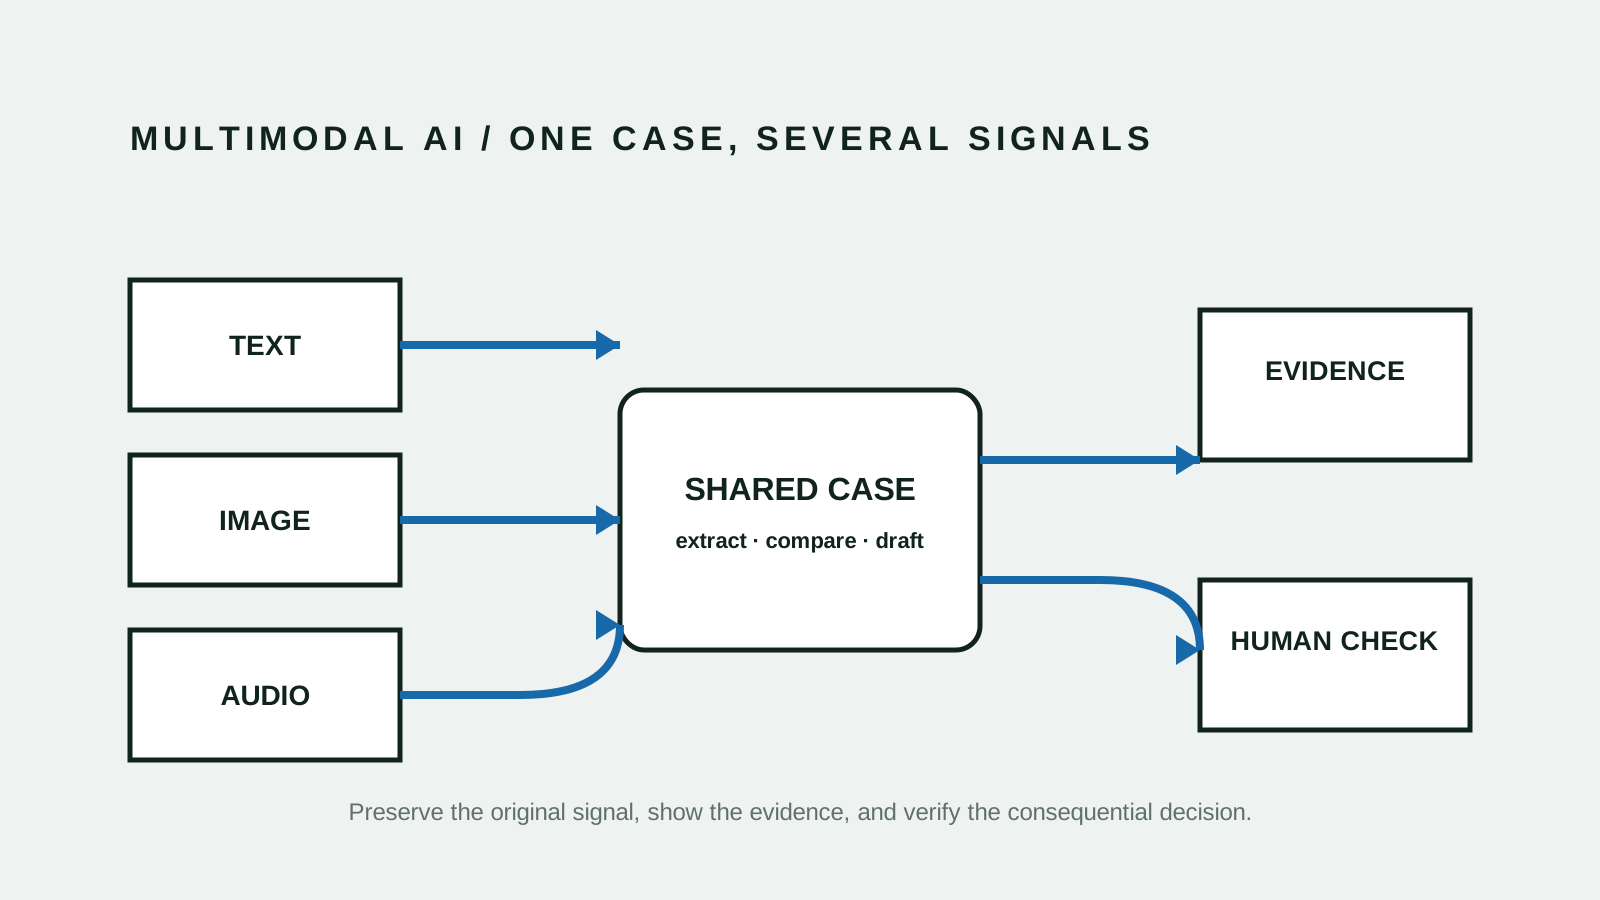
Multimodal AI can combine text, images, audio and video inside one case, but useful adoption depends on preserving evidence, protecting data and keeping people at consequential decisions.
Read article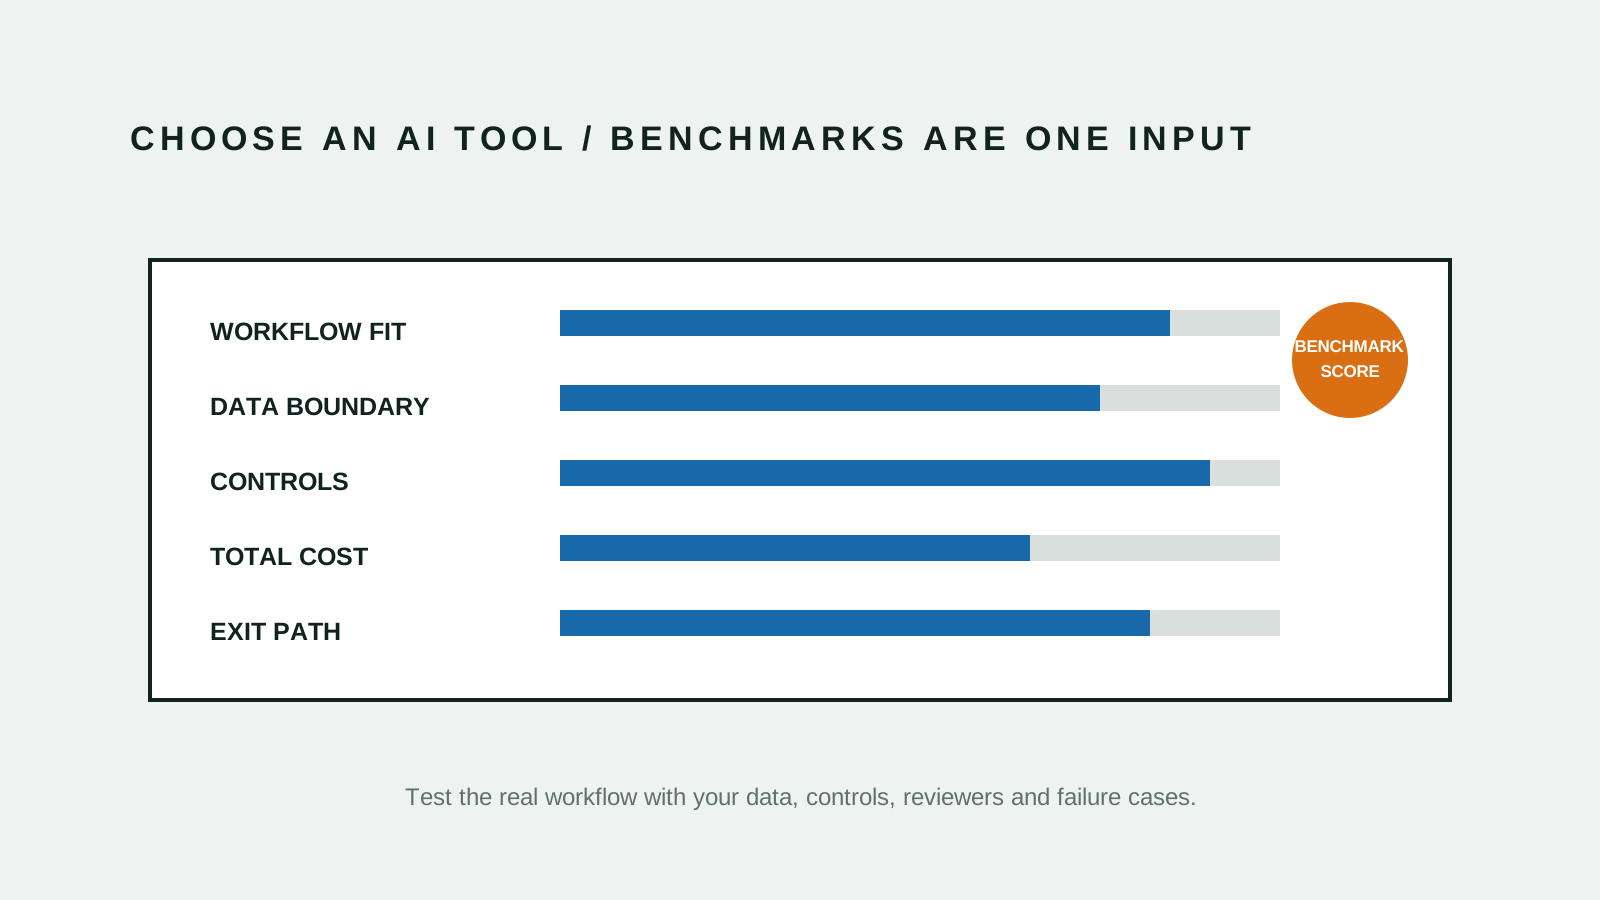
Benchmarks can compare a controlled capability, but Australian organisations should select AI tools by workflow fit, data boundaries, controls, operating cost and the ability to exit.
Read article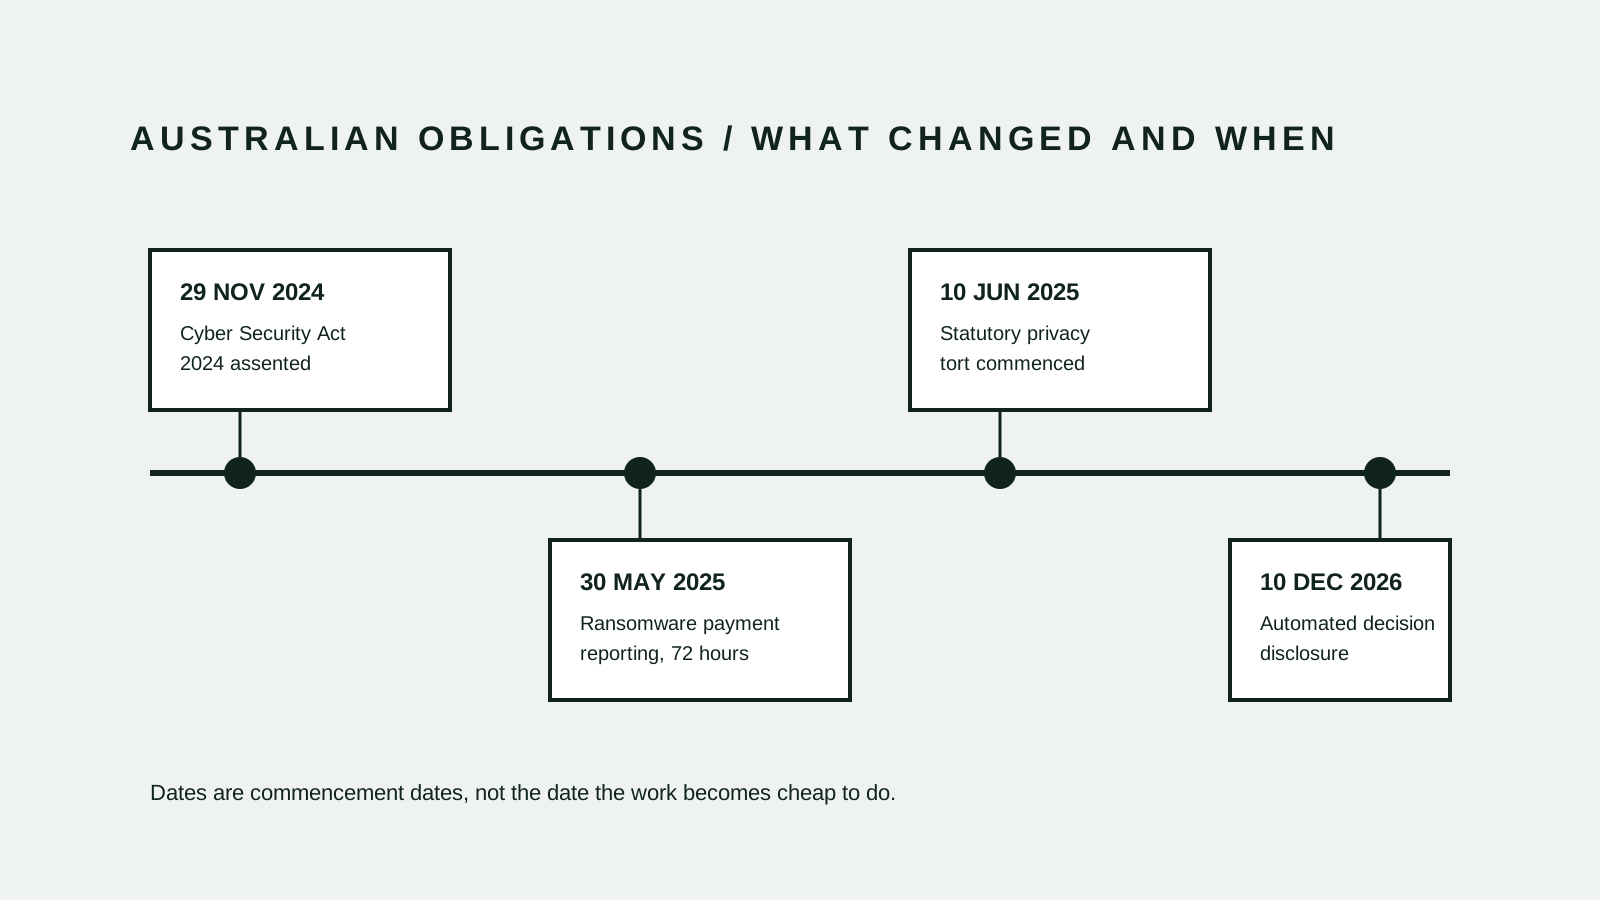
Three Australian obligations now sit inside ordinary software decisions: a privacy claim the regulator does not administer, ransomware payment reporting on a 72-hour clock, and automated decision-making disclosure from 10 December 2026.
Read article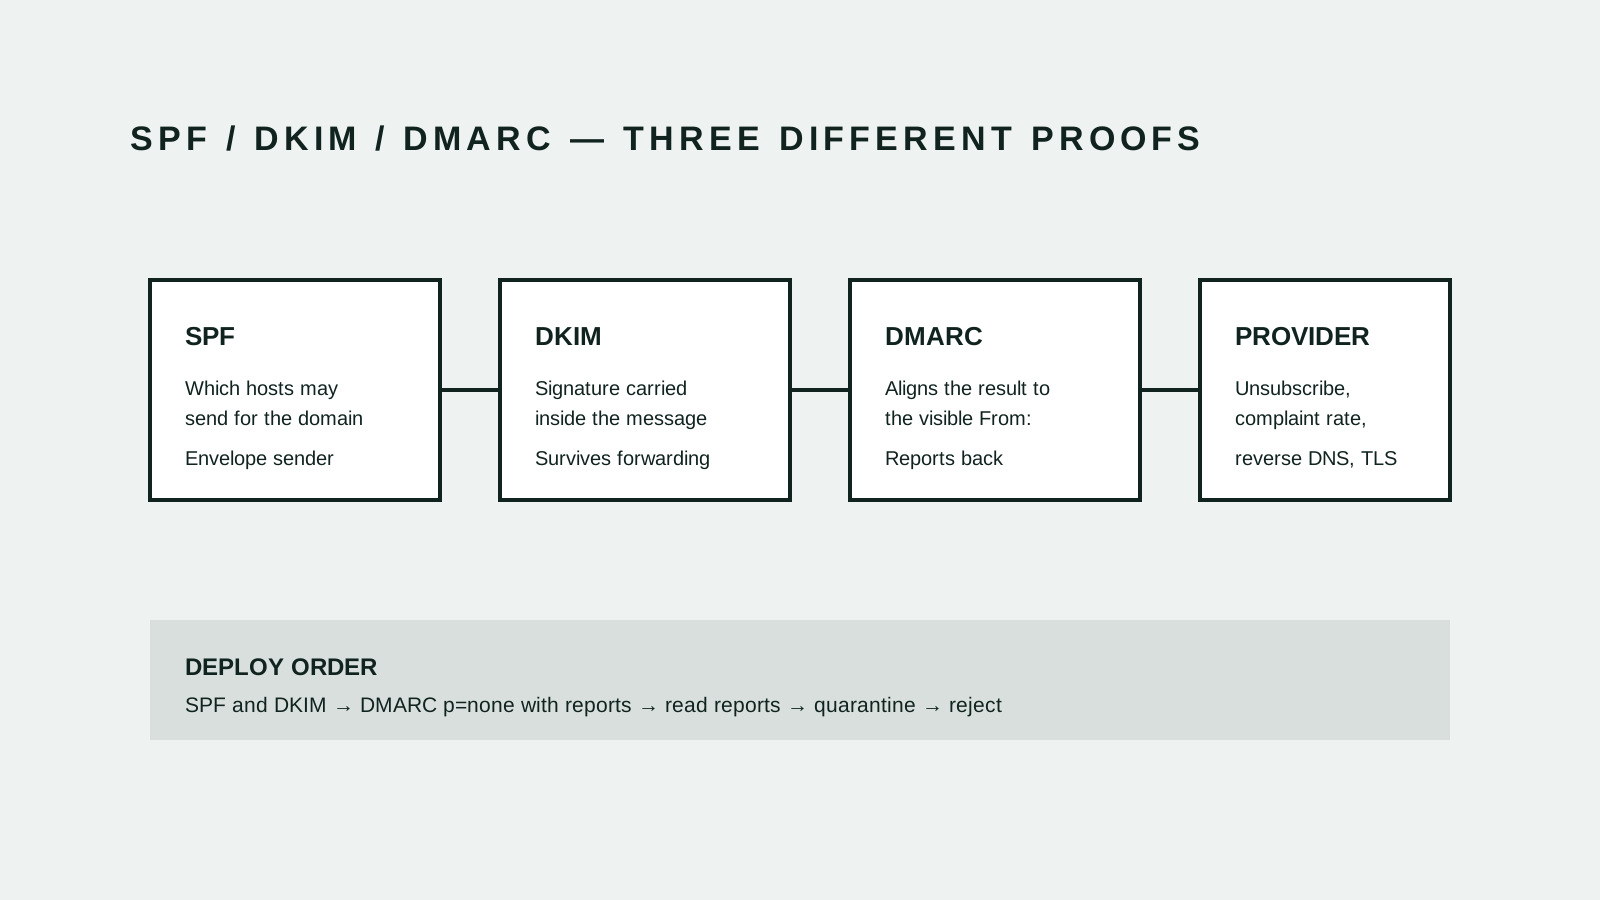
SPF, DKIM and DMARC each prove something different about a message. What each one actually checks, the order to deploy them without breaking mail, and why the forgotten sender is almost always the cause.
Read article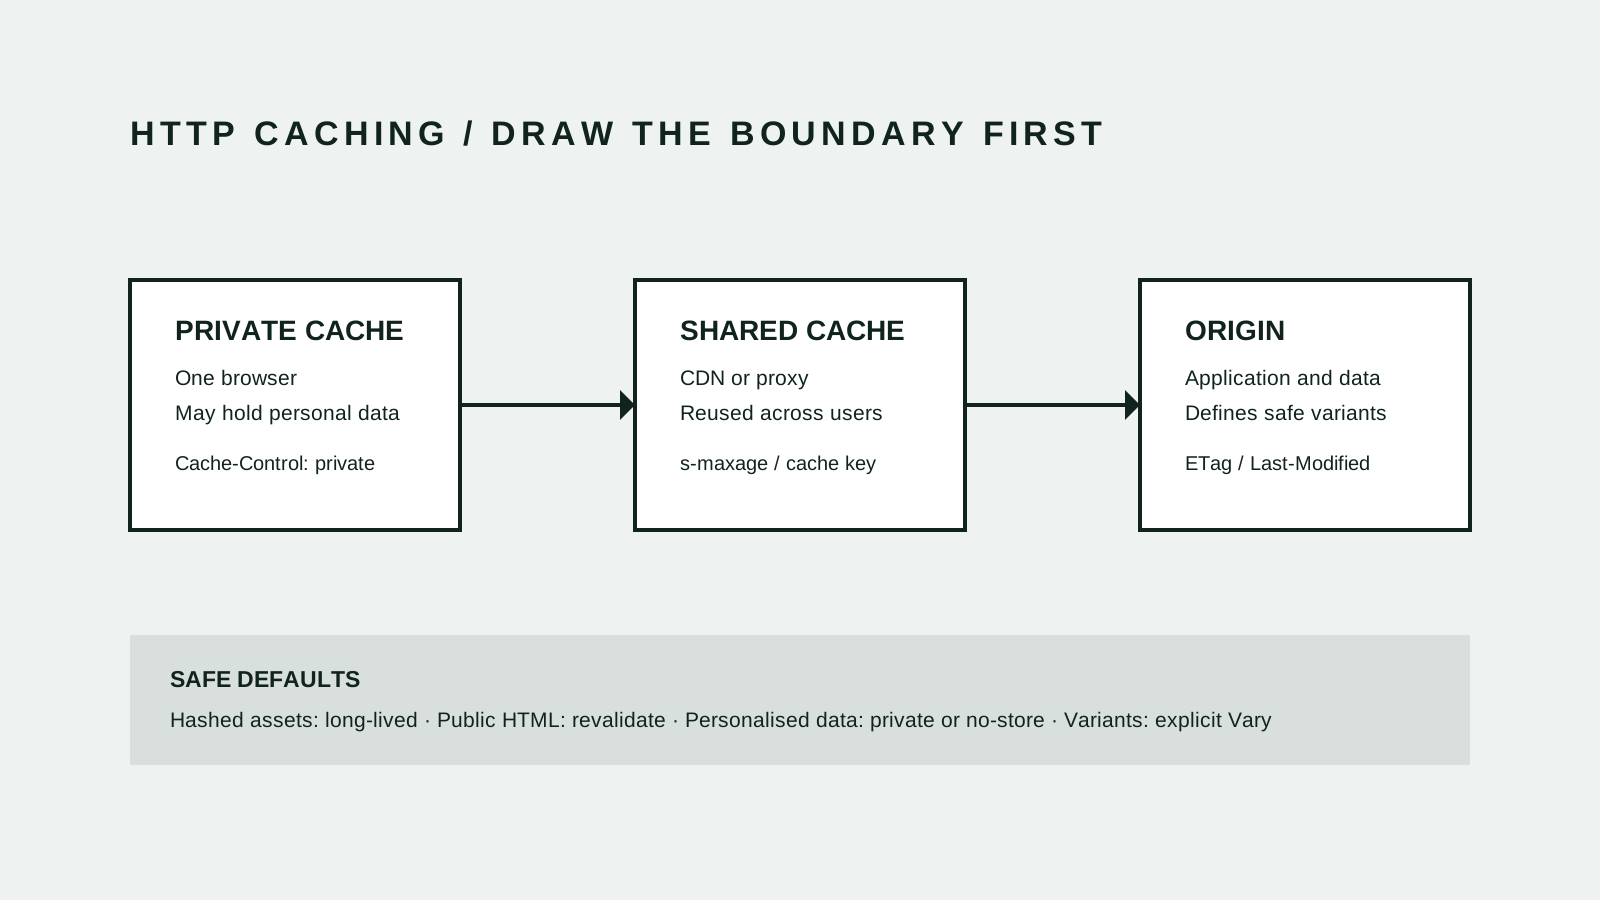
A practical way to separate browser and shared caches, choose Cache-Control directives, define cache keys and verify that faster delivery does not cross a user or content boundary.
Read articleA useful first conversation is enough to define the problem and the next decision.
Start a conversation